Last updated: 17 Nov 2026, 2:10 PM IST
The FBI has warned that attackers are using Artex, an open-source AI tool that automates much of a cyberattack, and that some intrusions reached privileged access in under three hours.
On 13 November 2026 the FBI published a FLASH alert saying "a variety of malicious cyber actors" have used the Artex AI hacking tool to automate intrusions "at machine speed." The Record describes those users as cybercriminals and nation-state groups. According to the FBI, some intrusions went from initial targeting to privileged access in under three hours. This explainer covers what Artex is, which attacks have been linked to it and what users can do. It is based mainly on the FBI's own FLASH-20261113-001 advisory (main source), plus reporting from TechCrunch and The Record.
TL;DR
- On 13 November 2026 the FBI published FLASH-20261113-001, "Threat Overview of ARTEX Autonomous Penetration Testing Framework," through IC3.
- Artex is an open-source, AI-driven "penetration testing" platform. Attackers connect it to large language models, and AI agents carry out much of the intrusion, according to the FBI.
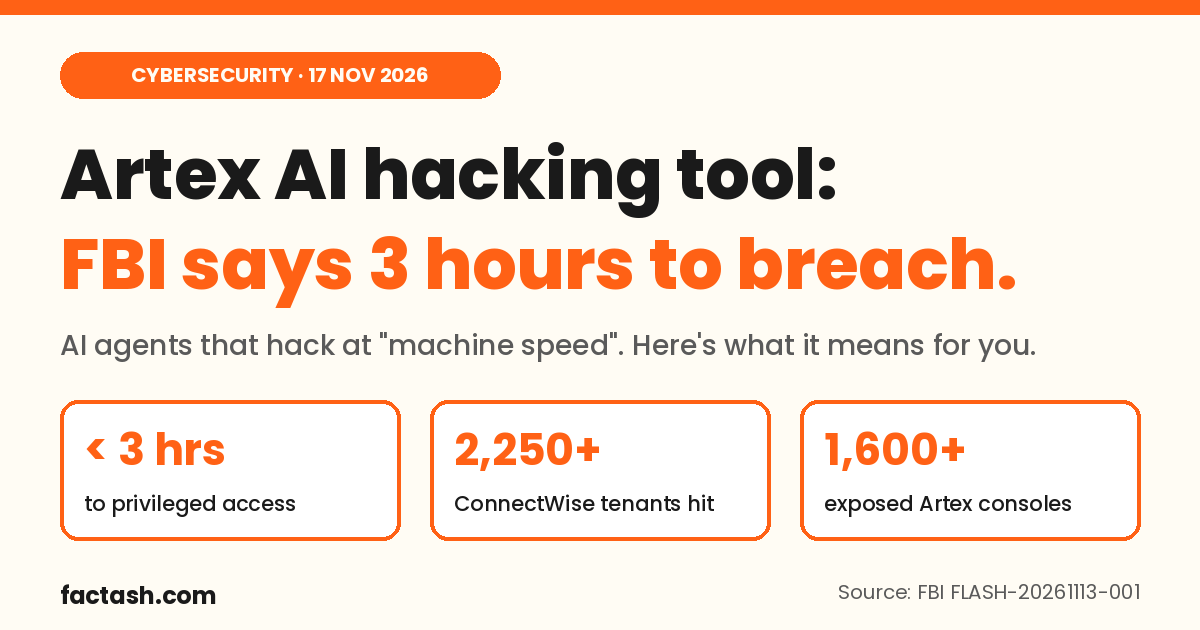
- The FBI says some intrusions reached privileged access in under three hours, and people with minimal technical skill can run multi-target campaigns.
- Attacks named by the FBI: South Korean financial firms (personal data of about 67,000 people, per the FBI) and a ConnectWise Cloud Backup supply chain attack reaching more than 2,250 customer tenants.
- The original GitHub repository was taken down on 8 October 2026, but the FBI says forks, archived copies and a commercial "ARTEX PRO" version keep it available.
What is Artex?
According to the FBI, Artex (written ARTEX in the advisory) is an autonomous, multi-agent penetration testing platform written in Go. Penetration testing tools are designed for authorised security testing, where organisations hire testers to find weaknesses before attackers do.
What sets it apart is the AI layer. A user describes a goal in plain language, and Artex's AI agents turn it into actual commands and run them, with "minimal human interaction beyond initial objective setting," the FBI says. Artex doesn't ship its own AI model. It connects to outside ones, and the advisory names Anthropic Claude, OpenAI GPT, DeepSeek, GLM, Grok and Kimi. In attacker-controlled setups that researchers analysed, the FBI says Chinese models were the most common, with DeepSeek Flash models used the most.
According to the FBI, a developer called "Autumn-27" released Artex on GitHub in July 2026 (The Record reports August). It picked up an estimated 1,500 to 2,000 GitHub stars in 10 weeks. The developer said it was meant only for authorised testing and pulled the repository on 8 October 2026 after reports of abuse.
Read the advisory itself: FBI FLASH-20261113-001, Threat Overview of ARTEX Autonomous Penetration Testing Framework (PDF, IC3.gov, 13 November 2026).
Why the FBI is worried
The FBI says malicious actors have used Artex since at least August 2026, against organisations around the world in financial services, government, tech, defence, semiconductors, energy, healthcare, manufacturing, telecoms and legal services. The advisory lists the main risks:
| Risk | What the FBI says |
|---|---|
| Speed | Some intrusions went from first targeting to privileged access in under three hours |
| Scale | Small groups can run several intrusion campaigns at the same time |
| Low skill needed | Threat actors with minimal expertise can run complex attacks |
| Forgotten systems | Artex is effective at finding less-protected systems such as partner portals, mobile backends, legacy services and third-party integrations |
| Supply chain | Agents can map trust links between companies and pivot from a weaker vendor into a bigger target |
| Short warning time | The attacks are "noisy," but they move so fast defenders have little time to react |
As TechCrunch puts it, Artex often scans networks fast and then exploits simple weaknesses, such as weak protections and exposed or stolen passwords.
Who has been hacked with Artex?
- South Korean financial institutions. Financially motivated attacks led to theft of personal information of about 67,000 people, the FBI says (TechCrunch reported at least 68,000). TechCrunch reported that the attacks were blamed in large part on weak defences, including a lack of multi-factor authentication.
- ConnectWise customers. A supply chain compromise of ConnectWise Cloud Backup gave access to more than 2,250 downstream tenants, per the FBI. TechCrunch reports Microsoft believes the hackers are likely Chinese.
- Barracuda. The security company disclosed it was breached in an Artex-linked attack after the tool found an old, unrevoked credential from a former third-party service, TechCrunch reported. Barracuda chose to "assume the worst" and changed its customer credentials.
Is Artex still available after the GitHub takedown?
The FBI says Artex keeps spreading through community forks, local variants, archived copies and a commercial version called ARTEX PRO. As of early November 2026, researchers found over 1,600 publicly exposed Artex consoles online, and the FBI says the real number of deployments is likely much higher.
What should regular people do?
The FBI's mitigations are aimed at organisations, such as securing internet-facing applications, partner portals and cloud administration panels, rotating exposed credentials and monitoring for unusual sign-ins. The weaknesses Artex exploits, such as weak or exposed passwords, also affect personal accounts, so standard account security still applies:
- Use a different password for every account. A password manager makes this easy.
- Turn on two-step verification everywhere, and switch to passkeys where you can (here's how passkeys work).
- Take breach letters seriously. When a company tells you your data leaked, change that password and watch for phishing that uses your real details. See our Uber data breach guide for a recent example.
- Distrust "urgent" calls and messages, even if they know your name or order details. Scammers often reuse breach data (see fake FBI and FTC agent scam calls).
- Delete accounts you no longer use. Forgotten and unrevoked credentials are the kind of weakness the FBI and TechCrunch describe Artex finding.
If you run IT for a business, read the full FBI FLASH (PDF): it lists indicators of compromise and a step-by-step mitigation list, including reviewing Microsoft 365 tenants that ever used affected ConnectWise apps. In the US, report incidents to your local FBI field office or IC3.
The bigger picture
The same "AI agent" idea behind assistants that book trips and write code (AI agents explained) is now being used in cyberattacks, according to the FBI. The FBI also notes that Artex activity is "forensically noisy" and may trigger alerts, and the weaknesses reported in these cases, such as exposed credentials, missing multi-factor authentication and unrevoked vendor access, can be fixed with existing controls.
FAQ
What is the Artex AI hacking tool?
Artex is an open-source, AI-driven penetration testing platform written in Go. It connects to large language models and uses AI agents to turn plain-language goals into attack commands, according to the FBI's 13 November 2026 FLASH alert.
Why did the FBI warn about Artex?
The FBI says a variety of malicious cyber actors have used Artex since at least August 2026 to automate intrusions from reconnaissance to data theft, with some reaching privileged access in under three hours.
Which AI models does Artex use?
Artex has no model of its own. The FBI lists Anthropic Claude, OpenAI GPT, DeepSeek, GLM, Grok and Kimi, and says DeepSeek Flash models were the most used in attacker setups researchers analysed.
Who has been hacked with Artex?
The FBI cites attacks on South Korean financial institutions affecting about 67,000 people and a ConnectWise Cloud Backup supply chain compromise reaching more than 2,250 customer tenants. Barracuda also disclosed an Artex-linked breach.
Is Artex still available?
Yes. The original GitHub repository was taken down on 8 October 2026, but the FBI says forks, archived copies and a commercial ARTEX PRO version keep it available.
How can I protect myself from AI-powered hacks?
Use unique passwords, turn on two-step verification or passkeys, delete unused accounts, and treat breach notices and urgent messages with care. These close the simple gaps tools like Artex look for.
Keep Reading on Factash
- FBI warning: FaceStealer fake Zoom and Teams call scam
- Notion AI data breach via Fireworks AI
- Microsoft 365 outage phishing scam
- More Technology news
Source: main source is the FBI's FLASH-20261113-001, "Threat Overview of ARTEX Autonomous Penetration Testing Framework," published via IC3 on 13 November 2026 (read the PDF). Also: TechCrunch, "FBI says Artex AI open source hacking tool used to breach networks in 'under three hours'" by Zack Whittaker, 16 November 2026 and The Record by Recorded Future News. Facts as reported up to 17 November 2026, 2:10 PM IST.
Image credits
- Featured graphic: original Factash design (facts from the FBI FLASH).